
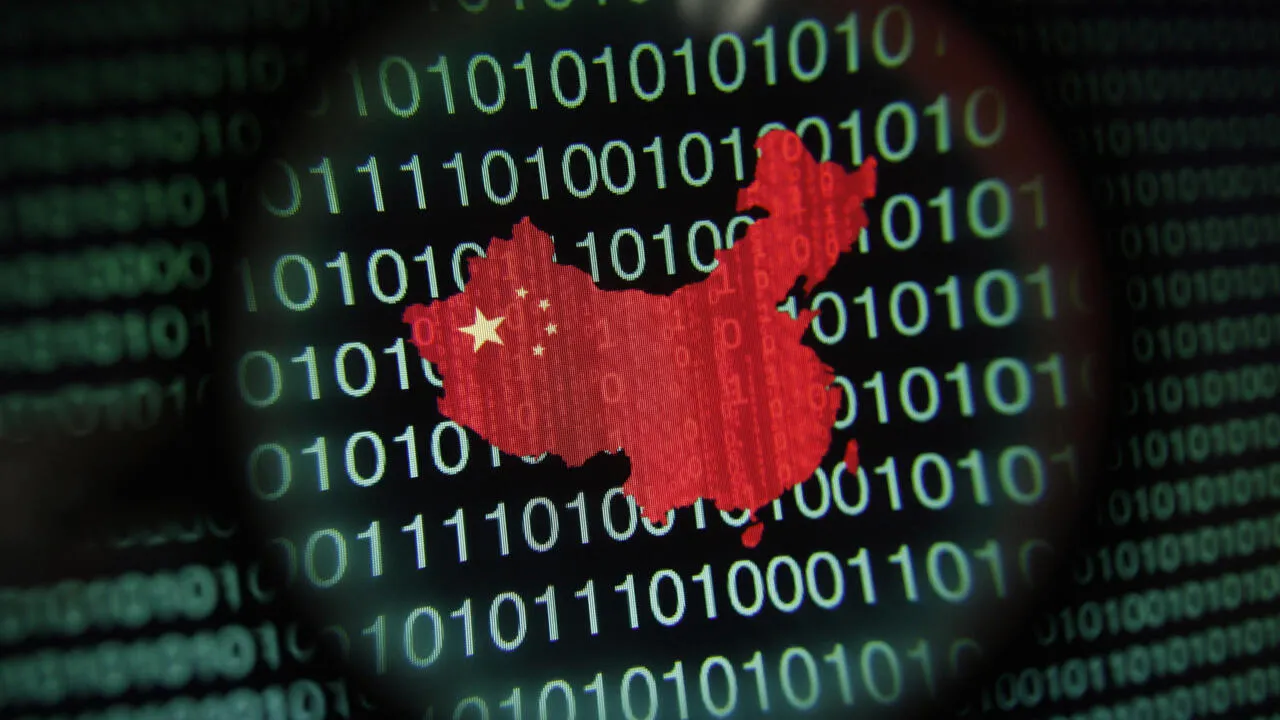
Chinese-linked hackers have targeted prominent U.S. artificial intelligence specialists through phishing campaigns, including an operation in which the attackers allegedly posed as a former White House technology official, according to a new report.
Cybersecurity firm Proofpoint said Thursday that the group, which it identifies as TA419, has been conducting credential-theft campaigns since at least 2025. The targets have reportedly included individuals affiliated with U.S. and Japanese think tanks, defence contractors, universities and law firms.
According to Proofpoint, one campaign in July 2026 involved the hackers impersonating Lynne Edwards Parker, a former Principal Deputy Director of the White House Office of Science and Technology Policy.
In a separate operation, the group reportedly assumed the identity of Heidi Crebo-Rediker, an economist and foreign policy specialist.
Proofpoint said the campaigns initially relied on seemingly legitimate professional outreach. Targets were invited to participate in a fictitious “AI Policy Advisory Committee” or asked to contribute to a purported Senate Foreign Relations Committee report concerning artificial intelligence export controls and supply chains.
The approach was designed to establish credibility before moving the interaction toward credential theft.
Once a target responded, Proofpoint said the attackers would provide a malicious or deceptive URL intended to facilitate access to the victim's cloud account.
The campaigns highlight the growing use of social engineering and impersonation against individuals involved in sensitive discussions surrounding artificial intelligence, technology policy, national security and international trade.
Source: www.foxnews.com
 Dr. Leila Haddad
 Elena Petrova
 Sofia Lindqvist
 James Mwangi